HIPAA Compliance Checklist for Small Healthcare Practices

Kelli Ngariki • September 5, 2024

10-Point HIPAA Checklist

HIPAA Practice Compliance Checklist with checkboxes, title, and logo.

Staying compliant with HIPAA (Health Insurance Portability and Accountability Act) can be daunting for small healthcare practices. With so many rules, regulations, and standards to keep track of, it’s easy to feel overwhelmed. However, ensuring the privacy and security of your patient’s health information is the law and a critical aspect of maintaining trust and professionalism in your practice.


To help simplify the process, we’ve compiled a comprehensive HIPAA compliance checklist for small healthcare practices. This guide will help ensure you cover all the key areas and comply with federal regulations.


1. Conduct Regular Risk Assessments

A HIPAA risk assessment helps you identify potential vulnerabilities in your practice’s handling of patient information. This includes assessing how you collect, store, and transmit Protected Health Information (PHI). Ensure your risk assessments are thorough and conducted at least annually or whenever significant changes to your systems occur.

Key Points:

  • Identify risks to PHI confidentiality, integrity, and availability.
  • Document all findings and develop a plan to mitigate risks.
  • Reassess risks regularly to stay ahead of potential threats.


2. Ensure Employee Training

HIPAA compliance is a team effort; all employees must understand the regulations. Regular training ensures that everyone in your practice, from front-office staff to healthcare providers, knows how to handle PHI properly and what to do in case of a data breach.

Key Points:

  • Conduct annual HIPAA training for all employees.
  • Provide role-specific training based on job duties.
  • Keep records of completed training sessions.


3. Implement Safeguards for Electronic PHI (ePHI)

The HIPAA Security Rule requires healthcare providers to implement safeguards to protect ePHI. These safeguards involve physical and technical measures to prevent unauthorized access to digital health information.

Key Points:

  • Use encryption to protect ePHI during transmission.
  • Implement secure access controls, such as strong passwords and multi-factor authentication.
  • Regularly update and patch software to address security vulnerabilities.


4. Create and Maintain HIPAA Policies and Procedures

Every small healthcare practice must have policies and procedures outlining how PHI is handled. These documents should cover everything from patient consent forms to how data breaches are reported and managed.

Key Points:

  • Ensure that policies are up-to-date and reflect current regulations.
  • Make these policies available to all employees.
  • Review and update your policies regularly.


5. Have a Breach Notification Plan

If a data breach occurs, HIPAA requires that you notify the affected patients and report the breach to the Department of Health and Human Services (HHS). A well-documented breach notification plan ensures you can respond quickly and correctly.

Key Points:

  • Develop a breach response plan that includes internal reporting and external notifications.
  • Know the timeline for breach reporting (within 60 days of discovery).
  • Keep patients informed of your actions to remedy the situation.\


6. Secure Physical Access to PHI

While much of HIPAA compliance focuses on digital data, physical security is just as important. Ensure that any paper records, filing systems, and workstations with access to PHI are secure.

Key Points:

  • Lock offices, filing cabinets, and storage rooms that contain PHI.
  • Limit access to areas where PHI is stored to authorized personnel only.
  • Implement clean desk policies to ensure no PHI is left unattended.


7. Maintain a Business Associate Agreement (BAA)

Small healthcare practices often work with third-party vendors, such as billing services or IT providers. You must have a signed Business Associate Agreement (BAA) if any of these vendors can access PHI. This document outlines the vendor’s responsibility to protect PHI and ensures they comply with HIPAA regulations.

Key Points:

  • Ensure all relevant vendors sign BAAs.
  • Review and update BAAs regularly to maintain compliance.
  • Keep records of all signed agreements.


8. Appoint a Privacy and Security Officer

Even small healthcare practices must designate someone responsible for overseeing HIPAA compliance. This could be a specific employee or an outsourced professional. The Privacy Officer handles compliance with the HIPAA Privacy Rule, while the Security Officer oversees compliance with the Security Rule.

Key Points:

  • Clearly define the roles and responsibilities of the Privacy and Security Officer.
  • Ensure they have the necessary training and resources to manage compliance.
  • Regularly review your practice’s compliance efforts with the appointed officer.


9. Monitor Access to PHI

One of the most important aspects of HIPAA compliance is ensuring that only authorized individuals have access to PHI. Implementing audit controls and monitoring systems can help you track access to both physical and digital records.

Key Points:

  • Implement audit trails to track who accessed or modified PHI.
  • Review access logs regularly for any suspicious activity.
  • Address unauthorized access immediately to prevent data breaches.


10. Regularly Review and Update Compliance Practices

HIPAA regulations can change, and new threats to patient data emerge over time. Regularly reviewing and updating your compliance practices is essential to staying compliant and protecting your patients’ information.

Key Points:

  • Schedule periodic reviews of your HIPAA policies and procedures.
  • Stay informed of any changes to HIPAA regulations.
  • Make updates as necessary to ensure your practice stays compliant.


Final Thoughts

HIPAA compliance doesn’t have to be overwhelming for small healthcare practices. Following this comprehensive checklist can create a solid foundation for protecting your patients’ health information and staying compliant with federal regulations. Regular assessments, employee training, and safeguarding both physical and electronic PHI are vital to ensuring your practice remains HIPAA compliant.

If you need assistance with HIPAA compliance or want to ensure your practice is fully protected, contact Healthcare Compliance Associates today. We specialize in making compliance simple, efficient, and stress-free for healthcare practices of all sizes.
By Kelli Ngariki August 18, 2026
If a needlestick happened today, would your team know exactly what to do next—or lose critical time figuring it out?
By Kelli Ngariki July 28, 2026
Small compliance mistakes can lead to big consequences. Learn what to watch for and how to protect your practice.
By Kelli Ngariki July 9, 2026
The largest healthcare fraud investigation in U.S. history offers valuable compliance lessons for small medical and dental practices. Here's what every practice owner and office manager should know.
By Kelli Ngariki June 18, 2026
If OSHA walked into your dental or healthcare office tomorrow, would your team know what to do?
By Ayana Guzzino May 12, 2026
HIPAA, IT, and Cybersecurity: What Healthcare Teams Need to Know
HIPAA Compliance for Healthcare Practices
By Kelli Ngariki April 21, 2026
HIPAA Compliance for Healthcare Practices starts with identifying hidden gaps. Learn the 3 hidden compliance gaps commonly found and how to address them.
By Kelli Ngariki April 14, 2026
Small dental and healthcare clinics have enough on their plate without worrying about OSHA citations. Beyond avoiding fines, workplace safety is essential for protecting your team and fostering a culture of care, responsibility, and professionalism. Whether you’re new to managing compliance or just need a refresher, here are five key OSHA must-haves for 2025: 1. Bloodborne Pathogens & Sharps Safety Train annually (yes, every year!) on how to handle exposure risks Keep a current Exposure Control Plan Offer the hepatitis B vaccine series and document refusals Ensure every employee with face-to-face patient contact has a documented TB test, as required for healthcare settings 2. Hazard Communication Make sure your team knows where SDS sheets are stored and how to read them Label secondary containers clearly Train new staff on chemical hazards—before their first exposure 3. PPE Use and Fit Gloves, eye protection, masks, gowns: who wears what, and when? Train staff on how to properly don and doff PPE Conduct hazard assessments to justify PPE use 4. Emergency Action Plans Fire evacuation, exit routes, and emergency contacts should be posted and known Conduct brief Emergency Action Plan refreshers annually (many offices forget this!) 5. OSHA Documentation & Inspection Prep Keep training logs, incident reports, and written plans accessible Know what to do if an inspector shows up—who talks to them, what documents to provide Bonus: Don’t Let OSHA Be a Surprise Most OSHA citations in small clinics are for things like: Failure to document regular safety meetings Missing training records No exposure control plan Blocked exits Failing to flush eye wash stations Why OSHA Compliance Matters More Than Ever in 2025 OSHA doesn’t have to be overwhelming. With a little preparation and the right tools, you can create a safe, compliant workplace and avoid costly mistakes. Want help with your OSHA binder, policies, or staff training? Reach out—we make compliance doable for busy healthcare teams. This post was drafted with assistance from AI and reviewed by a compliance professional to ensure accuracy and relevance for healthcare practices.
By Kelli Ngariki March 5, 2026
Learn what patching vulnerabilities means for dental and small healthcare practices, who owns it, how often to patch, and what OCR expects after ransomware.
People receiving HIPAA training; a man points to a screen displaying training information. Laptop open, server room in background.
By Kelli Ngariki February 18, 2026
Many tech companies and vendors don't realize HIPAA applies to them. Learn if you're a Business Associate and what training your workforce needs to avoid fines.
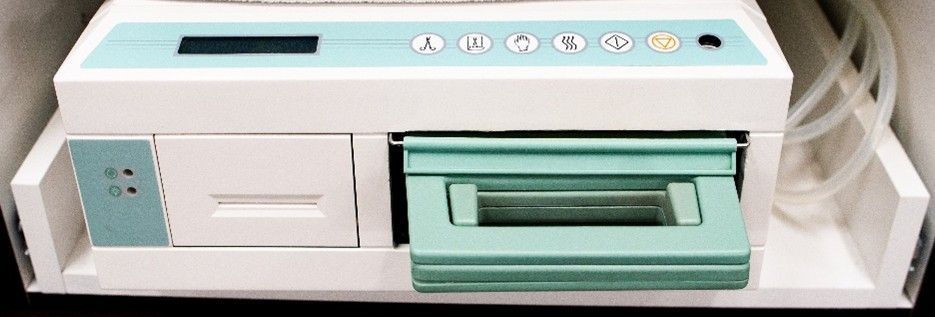
Medical device, white and teal, with a tray and control panel.
By Kelli Ngariki November 24, 2025
In fast-paced dental and medical clinics, it’s tempting to rely on a STATIM sterilizer—a type of immediate-use steam sterilizer—to quickly process instruments. But using this device appropriately is critical to patient safety and regulatory compliance. This post breaks down when and how to use STATIM sterilization based on CDC flash sterilization guidelines, helping small healthcare practices stay compliant without cutting corners. What Is an Immediate-Use Steam Sterilizer (STATIM)? A STATIM sterilizer is a specialized piece of equipment used for immediate-use steam sterilization (IUSS), formerly known as flash sterilization. It’s designed to rapidly sterilize medical and dental instruments that are urgently needed for patient care—not for routine or convenience-based use. When Is It Acceptable to Use a STATIM Sterilizer? According to CDC sterilization standards, STATIM use is acceptable only when: • The instrument is urgently needed and there’s no time to sterilize using standard packaging and storage methods. • It’s not being used to compensate for having too few instrument sets or to save time during busy periods. CDC Guidelines for Flash Sterilization: What You Must Do Following these steps will help you stay compliant with CDC and OSHA infection control requirements: 1. Limit Usage to Urgent Needs Only use STATIM sterilization for instruments needed immediately for patient care. 2. Do Not Use for Convenience Avoid using it as a way to speed up workflow or compensate for inadequate inventory. 3. Thoroughly Clean Instruments First All instruments must be fully cleaned and decontaminated before entering the STATIM cycle. 4. Do NOT Store Unwrapped Items After sterilization, transfer instruments (or handpieces) directly to the point of use in a sterile container or tray. Never store unwrapped items. 5. Use Approved Containers Only Only use flash sterilization containers or trays designed for high-temperature steam. 6. Monitor All Sterilization Cycles • Use biological indicators at least weekly. • Use chemical and mechanical indicators in every STATIM cycle. 7. Prevent Contamination During Transfer Maintain a clean transfer process. Ensure that items aren’t contaminated during handling or transport. Best Practices for STATIM Sterilizer Use in Dental and Medical Clinics • Keep backup instrument sets available to reduce reliance on immediate-use cycles. • Ensure staff are trained on STATIM operation and CDC sterilization protocols. • Document and log every STATIM cycle, including indicator results. • If your clinic is frequently using the STATIM for convenience or to keep up with patient flow, consider investing in an additional autoclave to support proper instrument processing and reduce compliance risks. Learn More from the CDC For detailed guidance on sterilization in healthcare settings, visit the CDC’s official page: 🔗 CDC Sterilization Guidelines Strong infection control isn’t just about guidelines— it’s about how your dental practice operates day to day. The way instruments are handled, PPE is used, and procedures are carried out in the clinical space affects both infection control and OSHA compliance. Issues in these areas are often identified during OSHA inspections, exposure incidents, or infection control reviews. Our FREE OSHA Compliance Risk Review helps dental practices understand how their safety and infection control efforts are functioning by identifying: Workflow or physical-space issues that may increase exposure risk OSHA gaps related to PPE, training, or exposure controls Areas where OSHA and CDC infection control expectations overlap It’s a simple, no-obligation way to confirm whether your safety systems support both staff protection and patient care. 👉 Schedule Your Free OSHA Compliance Risk Review